Huge cybersecurity leak lifts lid on world of China’s hackers for hire

A big leak of data from a Chinese cybersecurity firm has revealed state security agents paying tens of thousands of pounds to harvest data on targets, including foreign governments, while hackers hoover up huge amounts of information on any person or institution who might be of interest to their prospective clients.

The cache of more than 500 leaked files from the Chinese firm I-Soon was posted on the developer website Github and is thought by cybersecurity experts to be genuine. Some of the targets discussed include Nato and the UK Foreign Office.

Share

What is the dark web and what can you find on there?

During the trial of Brianna Ghey’s killers, the court heard an illuminating text exchange between the teenage murderers Scarlett Jenkinson and Eddie Ratcliffe.

Jenkinson had been fuelling her fantasies by accessing murder and torture videos on the dark web. “I love watching torture vids. Real ones on the dark web,” she told her friend. But she wanted more and asked Ratcliffe how to get hold of live videos of people being tortured, for which you had to pay. “Why would I know?,” Ratcliffe said.

Share

Notorious Russia gang claims it stole ‘classified and top secret documents’ from US intelligence agencies – as FBI warns China hackers are preparing to ‘wreak havoc’ in America

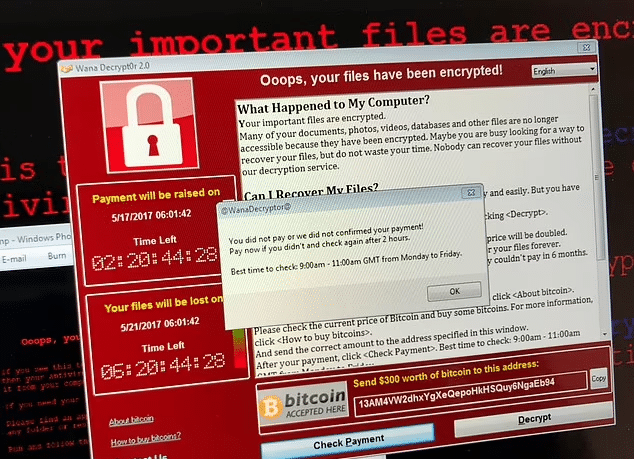
A Russian ransomware gang allegedly infiltrated a technology company responsible for handling top-secret documents from US intelligence agencies, like the FBI.

The notorious group Blackcat, also known as ALPHV, is threatening to release the classified documents if the company, Technica, does not contact them soon.

Technica is a veteran-owned company that provides technology solutions to support the Federal Government’s mission to defend and protect America.

Share

Authorities investigating massive security breach at Global Affairs Canada

Canadian authorities are investigating a prolonged data security breach following the “detection of malicious cyber activity” affecting the internal network used by Global Affairs Canada staff, according to internal department emails viewed by CBC News.

The breach affects at least two internal drives, as well as emails, calendars and contacts of many staff members.

CBC News spoke to multiple sources with knowledge of the situation, including employees who have received instructions on how the breach affects their ability to work. Some were told to stop working remotely as of last Wednesday.

h/t Mauser

Share

Huge data leak dubbed the ‘Mother of all Breaches’ sees 26 BILLION records leaked from sites including Twitter, Linkedin, and Dropbox

Your personal information may have been leaked in the ‘Mother of all Breaches’ (MOAB), cybersecurity researchers have warned.

Over 26 billion personal records have been exposed, in what researchers believe to be the biggest-ever data leak.

Sensitive information from several sites including Twitter, Dropbox, and Linkedin was discovered on an unsecured page.

Share

MGM Resorts: Slot machines go down in cyber-attack on firm

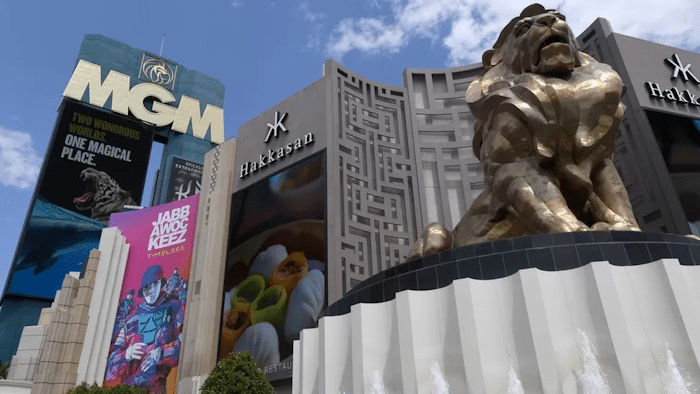
Customers have reported problems with slot machines and online room booking systems following a cyber-attack on casino and hotel giant MGM Resorts.

Certain systems were shut down due to a “cyber-security issue”, the firm said.

But it added that its facilities remained “operational”.

One customer at the MGM Grand in Las Vegas said she had walked into the wrong room because the hotel’s digital keys were malfunctioning, and said staff had to distribute physical keys.

Share

Cybercrime set to threaten Canada’s security, prosperity, claims spy agency

Organized cybercrime is set to pose a threat to Canada’s national security and economic prosperity over the next two years, the national signal intelligence agency said on Monday.

The Communications Security Establishment (CSE) in a report identified Russia and Iran as cybercrime safe havens where criminals can operate against Western targets.

Share

Our cyberspace invaders: Why nobody can seem to solve Canada’s massive hacking problem

On a drab Wednesday in early February, malicious software from Russia quietly infiltrated the internal systems of Canada’s largest bookstore chain.

At the time, Indigo Books & Music Inc. IDG-T had recently promoted a new chief executive, and a major upgrade of the company’s decades-old website was just wrapping up. The retailer was implementing grand plans to expand its offerings, looking beyond books and launching into a wide array of markets around the world.

Share

Twitter admits to ‘security incident’ involving Circles tweets

A privacy breach at Twitter published tweets that were never supposed to be seen by anyone but the poster’s closest friends to the site at large, the company has admitted after weeks of stonewalling reports.

The site’s Circles feature allows users to set an exclusive list of friends and post tweets that only they can read. Similar to Instagram’s Close Friends setting, it allows users to share private thoughts, explicit images or unprofessional statements without risking sharing them with their wider network.

Share

Citizen Lab warns of new “Zero click” Pegasus like Israeli spyware threat targeting journalists and political figures

Security experts have warned about the emergence of previously unknown spyware with hacking capabilities comparable to NSO Group’s Pegasus that has already been used by clients to target journalists, political opposition figures and an employee of an NGO.

Researchers at the Citizen Lab at the University of Toronto’s Munk School said the spyware, which is made by an Israeli company called QuaDream, infected some victims’ phones by sending an iCloud calendar invitation to mobile users from operators of the spyware, who are likely to be government clients. Victims were not notified of the calendar invitations because they were sent for events logged in the past, making them invisible to the targets of the hacking. Such attacks are known as “zero-click” because users of the mobile phone do not have to click on any malicious link or take any action in order to be infected.

Share

International sting on the ‘world’s biggest fraudsters paradise’ stealing YOUR passwords: Criminal ‘online market’

An ‘Amazon for crime’ online marketplace selling millions of sets of stolen personal information for 56p each has been blown open by UK and international investigators.

A sting on the site – which was called Genesis Market – unfolded last night and saw raids on users across the globe.

It was led by the FBI and Dutch police forces and 17 other countries, including the UK’s National Crime Agency (NCA), which made 24 arrests in and around Grimsby.

Share

Revealed: the hacking and disinformation team meddling in elections

A team of Israeli contractors who claim to have manipulated more than 30 elections around the world using hacking, sabotage and automated disinformation on social media has been exposed in a new investigation.

The unit is run by Tal Hanan, a 50-year-old former Israeli special forces operative who now works privately using the pseudonym “Jorge”, and appears to have been working under the radar in elections in various countries for more than two decades.

He is being unmasked by an international consortium of journalists. Hanan and his unit, which uses the codename “Team Jorge”, have been exposed by undercover footage and documents leaked to the Guardian.

Share

Whistleblowers allege U of T data project collected 600,000 patient records without consent

Ontario’s privacy commissioner is investigating a sweeping data project at the University of Toronto that is alleged to have collected over 600,000 electronic medical records without patient consent or knowledge.

… Access to that giant database is then sold or shared with researchers and other “third parties,” according to a copy of the complaint obtained by Global News.

Share

Twitter in data-protection probe after ‘400 million’ user details up for sale

A watchdog is to investigate Twitter after a hacker claimed to have private details linked to more than 400 million accounts.

The hacker, “Ryushi”, is demanding $200,000 (£166,000) to hand over the data – reported to include that of some celebrities – and delete it.

… The data is said to include phone numbers and emails, including those belonging to celebrities and politicians, but the purported size of the haul is not confirmed. Only a small “sample” has so far been made public.

The Guardian reported that data of US Congresswoman Alexandria Ocasio-Cortez was included in the sample of data published by the hacker. The data of broadcaster Piers Morgan, who recently had his Twitter account hacked, is also reported to be included.

Share